How to Connect to Instances with SSH
Checked on 30 October 2026 using OpenSSH and public-key authentication on an Ubuntu 24.04.5 LTS Instance. The connection used the root account on that image; other images can use a different login account.
Prepare the connection
Before connecting, have these ready:
- An active Instance and its public IP address from the Instances page.
- The login username for the selected operating-system image.
- The private key matching the public key selected when you created the Instance.
- Network access from your computer to the Instance's SSH port, normally TCP
22.
203.0.113.10 is a documentation placeholder throughout this guide. Replace it with your own Instance IP address. Replace root if your image uses another account.
Create an SSH key before creating the Instance
If you already have a suitable key pair, use its public key. Otherwise, create a dedicated Ed25519 key on your own computer. If the filename below already exists, choose a different filename; do not overwrite an existing private key. Enter a strong passphrase when prompted.
On Linux or macOS:
mkdir -p ~/.ssh
chmod 700 ~/.ssh
ssh-keygen -t ed25519 -a 64 -f ~/.ssh/fibacloud_instances_ed25519 -C "fibacloud-instances"
cat ~/.ssh/fibacloud_instances_ed25519.pub
On Windows with the OpenSSH client, use PowerShell:
New-Item -ItemType Directory -Force "$HOME\.ssh" | Out-Null
ssh-keygen -t ed25519 -a 64 -f "$HOME\.ssh\fibacloud_instances_ed25519" -C "fibacloud-instances"
Get-Content "$HOME\.ssh\fibacloud_instances_ed25519.pub"
Copy the complete public-key line, beginning with ssh-ed25519, into the SSH Key option when creating the Instance. Keep the file without .pub on your computer: it is the private key and must not be uploaded to the control panel. Adding a key to your account later does not establish that it has been installed in an existing Instance.
Connect with OpenSSH
Open Terminal on Linux/macOS or PowerShell on Windows. ssh -V checks whether the client is installed. Windows does not require WSL or PuTTY to use OpenSSH; see Microsoft's OpenSSH installation instructions if the command is unavailable.
For the key created above, connect with:
ssh -i ~/.ssh/fibacloud_instances_ed25519 -o IdentitiesOnly=yes [email protected]
The equivalent PowerShell command is:
ssh -i "$HOME\.ssh\fibacloud_instances_ed25519" -o IdentitiesOnly=yes [email protected]
-i selects your private key; IdentitiesOnly=yes prevents an SSH agent from trying unrelated keys. Enter the key's passphrase if requested. A private-key passphrase is different from an operating-system password or your FibaCloud account password.
Verify the server identity
On first connection, OpenSSH displays the server's host-key fingerprint. Compare it with a value obtained through a trusted independent channel, such as an already trusted console session or a verified support response, before accepting it. If you cannot verify the identity, request help before continuing.
Once accepted, the host key is stored in your local known_hosts file. If a later connection reports that the host identification has changed, first check whether the Instance was rebuilt or restored and verify the new fingerprint. Do not disable host-key checking or delete a stored key just to silence the warning.
Check the session
After authentication, the shell prompt belongs to the Instance. These read-only commands confirm the account and operating system:
whoami
cat /etc/os-release
free -m
df -h /
The checked Ubuntu image accepted the selected SSH key and reported root. Guest-visible memory and filesystem sizes can differ from the plan's advertised RAM and disk capacity because of units and system reservations. Type exit to end the SSH session; this does not stop or cancel the Instance.
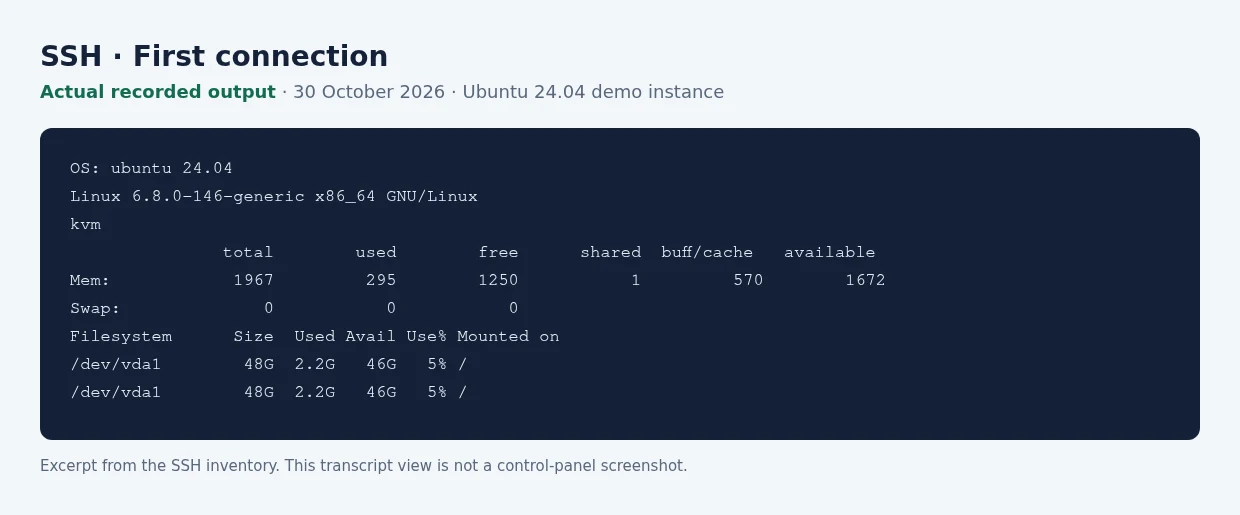
Excerpt from the actual SSH checks on the Ubuntu Instance. The recorded output is presented as a formatted transcript; memory usage and filesystem details can vary between Instances and over time.
Troubleshoot a connection
| Message or symptom | What to check |
|---|---|
| Connection timed out | Confirm the IP, running status, network reachability and any firewall rules affecting TCP 22. |
| Connection refused | The guest may still be starting or its SSH service may not be listening. Check the console. |
| Permission denied (publickey) | Confirm the image's username, the key selected at creation and the private-key path used with -i. |
| A password is requested unexpectedly | Check the selected key and username. Do not substitute the cloud-account password for an OS password. |
| Host identification has changed | Verify the server identity and any rebuild/restore before changing known_hosts. |
After restoring a snapshot, check the Instance's power state. If it is stopped, use Startup and allow the guest and SSH service time to start before retrying.
Connect with PuTTY
PuTTY is an alternative Windows client. The successful connection in this walkthrough used OpenSSH; the PuTTY settings below are a client reference, not a separately tested login. Use the official PuTTY download page and current manual for your installed version.
Configure PuTTY
Add the Instance IP and connection details
In Session, enter your Instance IP in Host Name (or IP address), set Port to 22, and select SSH.
Verify the SSH protocol
Use SSH version 2. Do not select Telnet or rely on screenshots of an older PuTTY interface.
Specify the matching private key
In current PuTTY versions, the key setting is under Connection → SSH → Auth → Credentials. Select the private key matching the public key installed on the Instance. If your version requires a .ppk file, import the OpenSSH private key locally with PuTTYgen and save it with passphrase protection; do not upload it or convert it with an online service.
Add the username
Under Connection → Data, set Auto-login username to the account for your image. root worked for the Ubuntu image checked here.
Save your preferences
Return to Session, name the connection under Saved Sessions, and select Save.
Connect
Load the saved session and select Open. Verify the host-key fingerprint before accepting the server identity, then unlock your private key if prompted. After login, run the same read-only checks shown above.